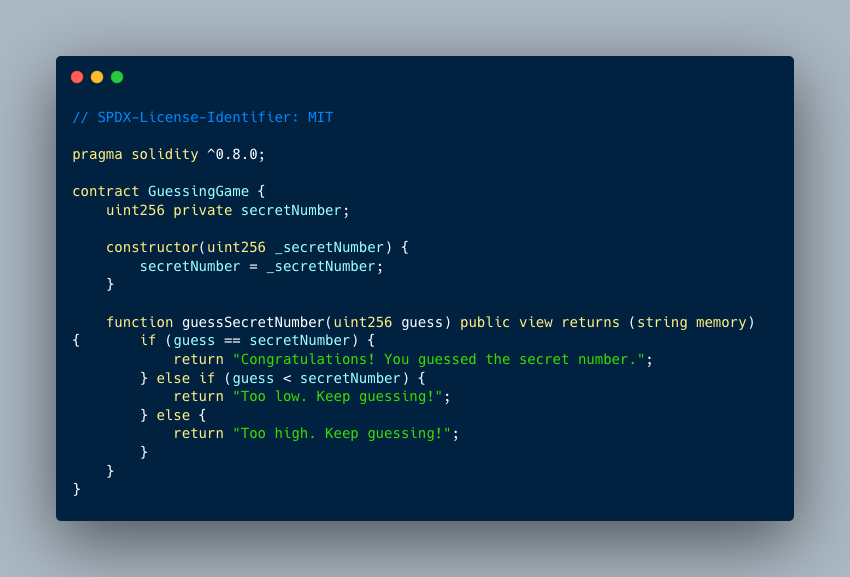
BTW @[email protected] was right. Anyone can view the contract deployment transaction and see the value of secretNumber that was passed as an argument to the constructor.
It is definitely a trick question and code intentionally made to be vulnerable to have fun finding what’s wrong and why it is bad practice to do so :)
For those that want to have an actual go at it: when deploying it with hardhat for example, you can pass in
Math.floor(Math.random()*1000)as the constructor argument in the deploy script, and then see if you can derive the number on the first guess.The formula will return a specific result of uint256 type which will be used in constructor on deployment, right? 😉
Yeah, this way you don’t know what the number is until you actually figure out the vulnerability.